Tag: auth

  • AWS – auto-join Windows clients to a managed AD

    Notes:

    • This post is part of a series: Part 1
    • I still consider this post a “snippet”, cause it is just a bit of – hopefully – copy-pastable Terraform code, with a bit of explanation.)

    All right. in the previous post we created a VPC including an AD, and configured route53 to forward requests regarding “AD stuff” to it. But, an AD is quite useless without Windows clients. And Windows clients are annoying, cause you have to join them to the AD. Luckily, there’s an automation for that.

    AWS introduced the AWS Systems Manager (formerly SSM), which is a small software component pre-installed on most (all?) AWS AMIs and connects to an AWS-internal management instance to perform actions. Like “domain auto-join”.

    Approach

    There are two ways to do this:

    1. Configure each host to join the AD, or
    2. Tell AWS to perform the auto-join action on every host with a certain tag

    I’m following option (2) here, using the tag key/value combination { "adjoin": "true" }. Easy.

    WARNING: AWS SSM was key in at least one massive data leak. SO BE VERY CAREFUL in how you use the Systems Manager and if in doubt refer to further documentation. I think this approach is safe, because we do not use any credentials in the following code.

    Having said that, let’s go.

    The code

    resource "aws_ssm_document" "ad_join_domain" {
      name          = "ad-join-domain"
      document_type = "Command"
      content = jsonencode(
        {
          "schemaVersion" = "2.2"
          "description"   = "aws:domainJoin"
          "mainSteps" = [
            {
              "action" = "aws:domainJoin",
              "name"   = "domainJoin",
              "inputs" = {
                "directoryId"    = aws_directory_service_directory.ad.id,
                "directoryName"  = aws_directory_service_directory.ad.name,
                "dnsIpAddresses" = aws_directory_service_directory.ad.dns_ip_addresses
              }
            }
          ]
        }
      )
    }
    
    resource "aws_ssm_association" "windows_server" {
      name = aws_ssm_document.ad_join_domain.name
      targets {
        key    = "tag:adjoin"
        values = ["true"]
      }
    }
    
    resource "aws_iam_role" "ad_autojoin" {
      name = "ad-autojoin"
      assume_role_policy = jsonencode({
        "Version" = "2012-10-17",
        "Statement" = [
          {
            "Effect" = "Allow",
            "Principal" = {
              "Service" = "ec2.amazonaws.com"
            },
            "Action" = "sts:AssumeRole"
          }
        ]
      })
    }
    
    # required it seems
    resource "aws_iam_role_policy_attachment" "ssm-instance" {
      role       = aws_iam_role.ad_autojoin.id
      policy_arn = "arn:aws:iam::aws:policy/AmazonSSMManagedInstanceCore"
    }
    
    # required it seems
    resource "aws_iam_role_policy_attachment" "ssm-ad" {
      role       = aws_iam_role.ad_autojoin.id
      policy_arn = "arn:aws:iam::aws:policy/AmazonSSMDirectoryServiceAccess"
    }
    
    resource "aws_iam_instance_profile" "ad_autojoin" {
      name = "ad-autojoin"
      role = aws_iam_role.ad_autojoin.name
    }
    

    The Windows instance

    Some notes:

    • NOTE: I am using a terraform module here, but in my code I am using a modified version of it. So it might be that this code needs some adjustments.
    • AWS does not yet provide Windows 10 images as AMIs. So we use Windows Server.

    Let’s go.

    data "aws_ami" "win2019server" {
      owners      = ["amazon"]
      most_recent = true
    
      filter {
        name   = "name"
        values = ["Windows_Server-2019-German-Full-Base*"]
      }
    
      filter {
        name   = "platform"
        values = ["windows"]
      }
    
      filter {
        name   = "architecture"
        values = ["x86_64"]
      }
    }
    
    module "ec2-instance" {
      source  = "terraform-aws-modules/ec2-instance/aws"
      version = "3.2.0"
    
      ami           = data.aws_ami.win2019server.id
      instance_type = "t3.large"
      cpu_credits   = "unlimited"
      subnet_id     = element(module.vpc.private_subnets, 0)
    
      # THIS IS WHAT WE NEED TO AUTO_JOIN!! :))
      iam_instance_profile = aws_iam_instance_profile.ad_autojoin.name
      tags                 = merge({ "adjoin" = "true" }, local.tags)
    
      # yes, weird syntax
      root_block_device = [{
        volume_size = 50
        tags = {
          Name = "my-root-block"
        }
      }]
    }
    

    References

  • AWS – create VPC and a managed AD with terraform

    Note:

    • This post is part of a series: Part 2

    AWS offers a managed AD service, in two flavors (Samba-based, and “original” Microsoft). This shows how you create …

    • a VPC
    • a managed Microsoft AD
    • an internal DNS zone
    • an internal DNS forwarder for the “AD domain” to the AD

    … with terraform.

    Let’s go.

    Part 1 – the VPC and the AD

    locals {
      name                  = "testproject"
      internal_dns_zone     = "testproject.local"
      ad_domain             = "testad.aws"
      cidr                  = "10.0.0.0/24"
      azs                   = ["eu-central-1b", "eu-central-1c"]
      database_subnets      = [cidrsubnet(local.cidr, 3, 0), cidrsubnet(local.cidr, 3, 1)]
      private_subnets       = [cidrsubnet(local.cidr, 3, 2)]
      public_subnets        = [cidrsubnet(local.cidr, 3, 3)]
      secret_winad_password = "uiuiuiui_super_secret"
      tags                  = { broughttoyouby = "flypenguin ;)" }
    }
    
    module "vpc" {
      source  = "terraform-aws-modules/vpc/aws"
      version = "3.7.0"
    
      azs                   = local.azs
      cidr                  = local.cidr
      create_igw            = true # for jump hosts, see also: https://is.gd/2Ry3H7
      database_subnets      = local.database_subnets
      enable_dns_hostnames  = true
      enable_nat_gateway    = true
      enable_vpn_gateway    = false # not yet
      name                  = local.name
      private_subnets       = local.private_subnets
      public_subnets        = local.public_subnets
      single_nat_gateway    = true
    }
    
    resource "aws_directory_service_directory" "ad" {
      name      = local.ad_domain
      password  = local.secret_winad_password
      edition   = "Standard"
      type      = "MicrosoftAD"
      tags      = local.tags
    
      vpc_settings {
        vpc_id     = module.vpc.vpc_id
        subnet_ids = module.vpc.database_subnets
      }
    }
    
    resource "aws_route53_zone" "vpc" {
      name = local.internal_dns_zone
    
      vpc {
        vpc_id = module.vpc.vpc_id
      }
    }
    

    Part 2 – the resolver

    Now this was pretty easy. Problem: Windows thinks it is responsible for performing autoritative (I think) DNS lookups for the AD “domain”. And the internal DNS resolver has absolutely no clue about any AD related stuff. Amazon itself offers two possibilities:

    1. using the managed AD as the primary DNS “servers”, forwarding requests to route53, or
    2. configure route53 to forward to the managed AD for requests regarding “testad.aws” (our AD “domain”)

    This describes option (1), because in my eyes the VPC should not stop functioning without the AD (which it does if you give the AD primary DNS responsibility).

    resource "aws_route53_resolver_endpoint" "ad_hcm_resolver" {
      name      = "ad-hcm-resolver"
      direction = "OUTBOUND"
      tags      = local.tags
    
      ip_address { subnet_id = module.vpc.database_subnets[0] }
      ip_address { subnet_id = module.vpc.database_subnets[1] }
    }
    
    resource "aws_route53_resolver_rule" "ad_fwd" {
      domain_name          = local.ad_domain
      name                 = "ad_hcm_forward"
      rule_type            = "FORWARD"
      resolver_endpoint_id = aws_route53_resolver_endpoint.ad_hcm_resolver.id
      tags                 = local.tags
    
      target_ip { ip = sort(aws_directory_service_directory.ad.dns_ip_addresses)[0] }
      target_ip { ip = sort(aws_directory_service_directory.ad.dns_ip_addresses)[1] }
    }
    
    # WE NEED THIS. without it does not work.
    resource "aws_route53_resolver_rule_association" "ad_fwd" {
      resolver_rule_id = aws_route53_resolver_rule.ad_fwd.id
      vpc_id           = module.vpc.vpc_id
    }
    

    WARNING: That stupid forwarder costs about 180$ / month (about 90¢ per IP address, and you must have two). It is REALLY expensive for what it does.

  • (AWS managed) AD – give local admin rights to domain users

    Note: This post is part of a series (Part 4):

    Situation: You have a bunch of systems in an (AWS managed) AD, and you want to give AD users local admin rights.

    Problem: You don’t know how.

    Solution: This post or this very nice video, or both.

    • Basically there are two ways.
    • One, you have an AWS managed AD, then you get …
    • Two, you don’t want to use the AWS groups or have a standard AD, then …
      • stick to the video.

    Hint: It’s easiest if you perform thost actions as the DOMAIN\Admin user, so you don’t have to enter that user’s password all the time.

  • Standard AD – auto-map a network drive

    Note: This post is part of a series (Part 3):

    Situation: You have this beautiful AD system, and you want to auto-map a network drive for your users using AD GPOs.

    Problem: You don’t know how.

    Solution: This post.

    • open group policy editor
    • create USER policy “AD GPO map network drive”
    • edit it
    • select “USER configuration / preferences / windows settings / drive maps”
    • right-click “new”
    • create share
    • you should force-apply the new GPOs on the target host using gpupdate /force

    Hint: It’s easiest if you perform thost actions as the DOMAIN\Admin user, so you don’t have to enter that user’s password all the time.

  • AWS managed AD – add user RDP permissions

    Note: This post is part of a series (Part 2):

    Situation: You have an AWS managed AD, some clients, and some AD users. Now the users should be able to log in to servers using RDP.

    Problem: Just by creating a user it does not have the appropriate permissions.

    Solution: Follow the AWS documentation or watch the AWS youtube video on the subject. This is basically it, with some screenshots and additional notes.

    Hint: It’s easiest if you perform thost actions as the DOMAIN\Admin user, so you don’t have to enter that user’s password all the time.

    • if you are paranoid check some local server configurations (it should already be correct though)
    • open AD user / group management
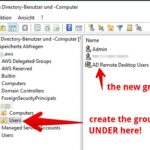
    • create a group
      • e.g. “AD Remote Desktop User” under Users/ in your domain
      • so if your domain is “domain.aws”, create it under “domain.aws/domain/Users/HERE”
    • add the user to the newly created group
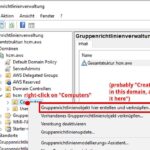
    • open group policy editor
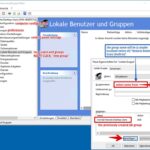
    • create new group under “computer configuration / preferences / control panel settings / local users and groups”
      • select Remote Desktop Users (built-in) FROM DROPDOWN!!!
      • add the previously created AD group as members
  • AWS managed AD – first steps after creation

    Note: This post is part of a series (Part 1):

    Situation: You have created a managed AD. Now you want to manage it.

    Problem: The servers probably don’t have the appropriate software installed.

    Solution:

    Hint: It’s easiest if you perform thost actions as the DOMAIN\Admin user, so you don’t have to enter that user’s password all the time.

  • Helm in a kops cluster with RBAC

    I created a K8S cluster on AWS with kops.

    I ran helm init to install tiller in the cluster.

    I ran helm list  to see if it worked.

    I got this:

    Error: configmaps is forbidden: User "system:serviceaccount:kube-system:default" \
        cannot list configmaps in the namespace "kube-system"
    

    That sucked. And google proved … reluctant. What I could figure out is:

    Causes

    • kops sets up the cluster with RBAC enabled (which is good)
    • helm (well, tiller) uses a standard role for doing things (which might be ok, at least it was with my stackpoint cluster), but in that case (for whatever reason) it did not have sufficient privileges
    • so we need to prepare some cluster admin roles for helm to use

    Fixes

    Just do exactly as it says in the helm docs 🙂 :

    • apply the RBAC yaml file which creates the kube-system/tiller service account, and binds this to the cluster-admin  role.
    • install helm with: helm init -service-account tiller

    Is that secure? Not so much. With helm you can still do anything to the cluster at all. I might get to this in a later post.

  • TeamCity LDAP authentication with JumpCloud

    JumpCloud looks like a great service to use LDAP without using LDAP. And I have just managed to find an error in the documentation, precisely the file “ldap-config.properties.dist”.

    The working configuration is:

    # basic jumpcloud url
    java.naming.provider.url=ldap://ldap.jumpcloud.com:389/
    
    # search user for jumpcloud
    java.naming.security.principal=uid=BIND_USER_NAME,ou=Users,o=ORG_ID,dc=jumpcloud,dc=com
    java.naming.security.credentials=BIND_USER_PASSWORD
    
    # unix ldap seems to use uid as username - see https://is.gd/dBPegr
    teamcity.users.login.filter=(uid=$capturedLogin$)
    teamcity.users.username=uid
    teamcity.users.base=ou=Users,o=ORG_ID,dc=jumpcloud,dc=com
    

    Seems to work nicely, now comes the finetuning.